Update Certificate Deployment for NovoOne Portal Domain
NovoOne Platform supports two domain certificate deployment modes, including automatic deployment via Let's Encrypt and manual certificate deployment. This topic describes how to modify certificate configurations to adopt your preferred certificate deployment mode.
Configure automatic certificate deployment
- Procedure
- Step 1. Enable automatic certificate deployment and obtain CNAME record on NovoOne Platform
-
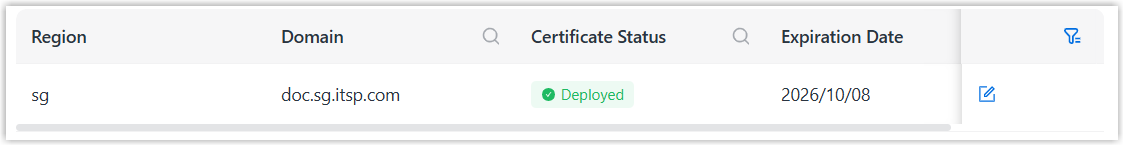
- Log in to NovoOne Platform portal, go to .
- Click
 beside the domain.
- In the Certificate Configuration section,
select Automatically issue certificate (Let's
Encrypt) of Certificate
Management.
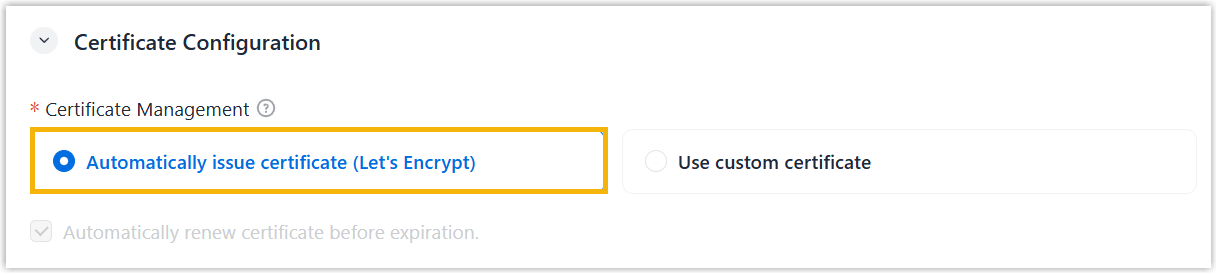
Once selected, the DNS Configuration section appears on the edit page.
- In the DNS
Configuration section, hover your mouse on the host
and target domains in the CNAME record list, then click
 to
copy and note down them for later use.Tip: For the host domain, the copy operation retrieves the subdomain portion for direct use in subsequent domain resolution. For example, the host domain is
_acme-challenge.doc.sg.itsp.com, only its subdomain portion_acme-challenge.doc.sgis copied for use.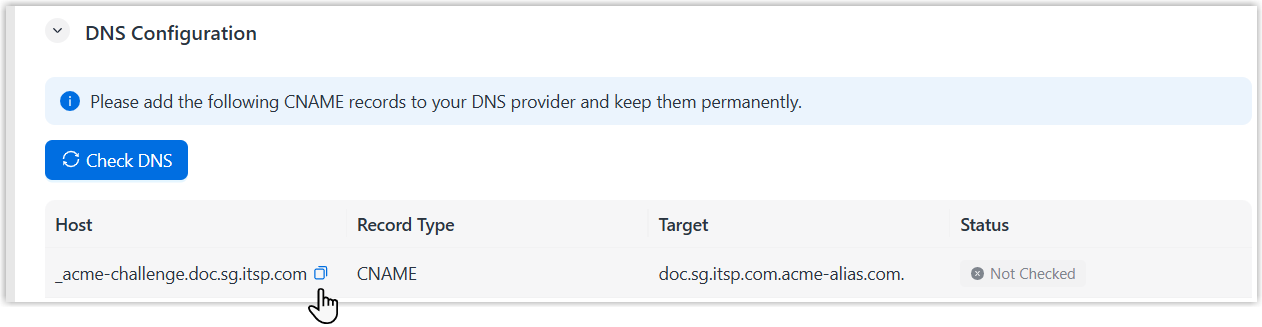
Leave this Edit Domains page open before proceeding.
- Step 2. Configure domain resolution on DNS server
- Add the CNAME records obtained from NovoOne
Platform to your DNS server to point your host domain to the corresponding
CNAME target domain.Note: For Host fields, your DNS provider will automatically append the root domain (
itsp.com). You only need to paste the raw data copied from NovoOne Platform portal into the field. - Step 3. Check resolution status and save settings on NovoOne Platform
-
- Back to Edit Domains page on NovoOne Platform portal.
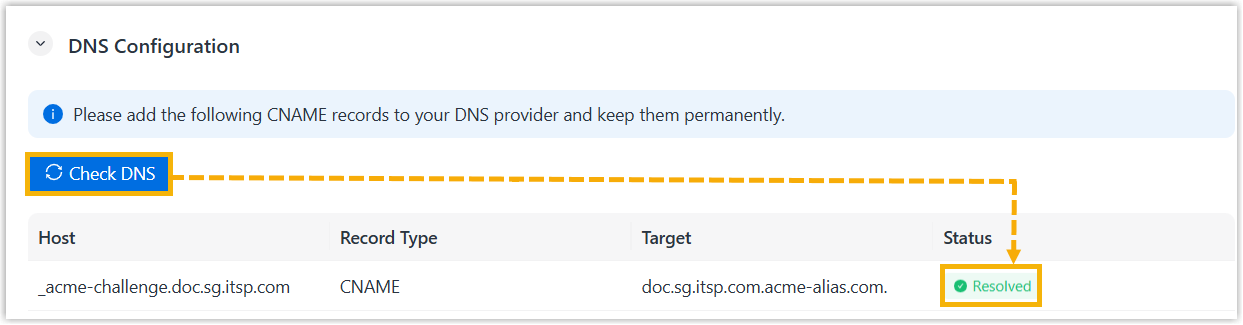
In the DNS Configuration section, click Check DNS at the left-top corner of the CNAME record list.
The status of the CNAME record displays Checking and switches to Resolved after approximately 3 seconds.
Note: The status may display Not Resolved due to DNS propagation delays. You can click Check DNS later to re-run the detection.If the status remains Not Resolved, review the previous Step 2.
- Click Save.
Configure manual certificate deployment
- Procedure
- Step 1. Prepare domain certificates from Certified Authority (CA)
-
Note: If you have purchased a wildcard SSL certificate covering the domain and it remains valid, you can skip this step and proceed to Step 2.
- Step 2. Enable manual certificate deployment on NovoOne Platform
-
- Log in to NovoOne Platform portal, go to .
- Click beside the domain.
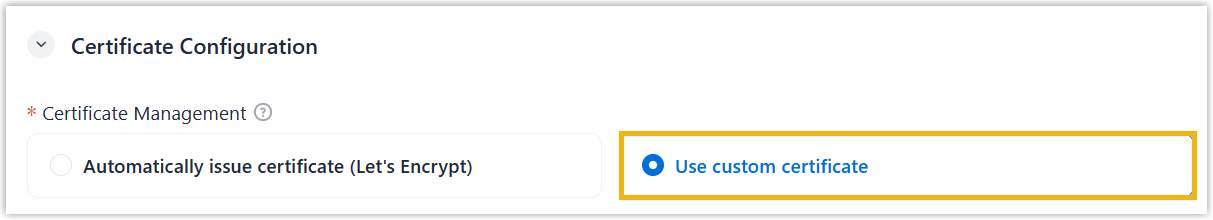
- In the Certificate Configuration section,
select Use custom certificate of
Certificate Management.
- In the Private Key field, fill in the
PEM-encoded private key downloaded from Certified Authority (CA) in
one of the following methods.Note:
- The supported content formats are as follows:
Format Description RSA Start with -----BEGIN RSA PRIVATE KEY-----and end with-----END RSA PRIVATE KEY-----.EC Start with -----BEGIN EC PRIVATE KEY-----and end with-----END EC PRIVATE KEY-----.PKCS#8 Start with -----BEGIN PRIVATE KEY-----and end with-----END PRIVATE KEY-----. - The content must not exceed 16 KB.
- Copy the content of the private key and enter it in the field directly.
- Click
 beside the field to upload the
private key file with the
.keyextension.The content of uploaded private key is displayed in the Private Key field.
- The supported content formats are as follows:
- In the Certificate field, fill in the
PEM-encoded certificate obtained from the Certificate Authority (CA)
in one of the following methods.Note:
- The certificate must contain a COMPLETE Certificate Chain assembled in the following order: the Server Domain Certificate , followed by Intermediate Certificates, and ending with the Root CA Certificate.
- The content must not exceed 32 KB.
- Copy the content of the certificate and enter it in the field directly.
- Click beside the field to upload the
certificate file with a
.cer,.crt, or.pemextension.The content of uploaded certificate is displayed in the Certificate field.
The certificate information (status, authority and expiration date) is auto filled in the Certificate Information section.
- If you intend to manually apply and upload certificates by yourself
before expiration, deselect the checkbox of Automatically renew
certificate before expirationNote: This setting is enabled by default. If enabled, the system will automatically issue and renew certificate via Let's Encrypt before expiration.
- Click Save.
Result